Raise the bar: 50 creative Cybersecurity Awareness Month ideas
The search is over! Our Cybersecurity Awareness Month guide is packed with ideas, examples, insights, and resources. Time to shine bright and make an impact.
Subscribe to the newsletter
Let’s be honest for a second …having technical security measures in place isn’t enough. It never was, and that isn’t about to change now. Not by a long stretch.
Sure, technical security measures might tick a box, keep your board happy (for a while), and they might even make a difference, temporarily. But that’s about it.
And here’s why this matters: every single year, millions of people deal with the fallout of cyberattacks. They cost organisations billions, and cause a whole lot of very real stress for real people.
If you’re reading this, you already get it. But knowing security matters and actually behaving securely during a busy workday are two very different things.
Why are we talking about this now? Because it’s Cybersecurity Awareness Month (CAM).
CAM has run every October since 2004. What started with the National Cybersecurity Alliance (NCA) 22 years ago has now grown into a massive global movement. And 2026 is shaping up to be the biggest yet.
Don’t make it easy for them
This year’s theme (Don’t make it easy for them) is refreshingly realistic.
Security isn’t about making one heroic, stress-induced decision under pressure. It’s about building a few tiny, repeatable habits during normal, everyday moments. If enough people do small things consistently, an attacker’s job gets a whole lot harder.
The campaign focuses on four core daily habits:
Using long, unique passwords: The NCA’s guidance for 2026 is specific: at least 16 characters, unique to every account, stored safely in an approved password manager.
Turning on multi-factor authentication (MFA): Enabling it everywhere it’s offered.
Scrutinising unexpected messages: Pausing on anything inbound that feels pushy, weird, or overly urgent …and (crucially) reporting it.
Keeping devices updated: Letting software updates run instead of hitting “remind me tomorrow” for two weeks straight. (We’ve all done it, no shade here.)
Is ‘Don’t make it easy for them’ the most human-friendly theme yet?
We all know we should eat more greens and sleep eight hours a night. But do we? …Some of us do, the rest of us try. But we know we should – that’s not the issue.
Lecture people? Doesn't work. Trick them with mean phishing tests? Backfires. Run campaigns that fight against basic human nature? Waste of budget.
CAM’s theme is human-friendly, because it’s all about simplicity, small steps, and routine. It works because it taps into basic psychology:
It cures security fatigue: Constant high alert is exhausting. Focus on tiny, manageable daily tasks instead.
It stays positive: Science shows that highlighting benefits works better than waving scary breach statistics in people's faces.
It values increments over overhauls: Micro-changes add up fast without overwhelming anyone.
It taps into social proof: When people see their teammates adopting secure habits, they naturally follow along.
We train our people all year. Why bother with CAM?
Fair question. But CAM isn't about routine compliance training. It is about momentum, community, and energy.
It’s about igniting excitement, and making people feel like they’re playing an active, important role in the solution.
Tackling human risk can feel like a slog, but you can’t afford to let campaign fatigue set in. Awareness month is your excuse to make security approachable, visible, and (dare we say it) fun.
The behavioural science cheat sheet for CAM
Want a campaign that actually lands? Tap into these proven psychological triggers:
1. Address human cognitive biases
We’re all wired with shortcuts. The availability heuristic makes us overreact to dramatic news headlines, while the bandwagon effect makes us click a link if we think ‘everyone else got this email too’. Call these biases out directly in your messaging so people catch themselves in the moment.
2. Segment your audience
Not everyone in your business speaks fluent IT. Tailor your message to different teams and knowledge levels. Don't worry about making it perfect …even basic segmentation delivers way higher engagement than a massive blast email.
3. Harness social influence
Give people space to share tips, talk through mistakes, and celebrate good habits. When security becomes a team topic rather than an IT rulebook, culture shifts.
4. Focus on immediate impact
Long-term risks (i.e. ‘our stock price might dip in 3 years’) feel abstract. Highlight short-term, personal consequences instead …like the hassle of locked accounts, lost work time, or personal data leaks.
5. Gamify and reward
Interactive quizzes, departmental escape rooms, and leaderboards turn boring topics into friendly competition.
6. Inspire autonomy over compliance
Nobody likes being micromanaged. Empower your team to take personal pride in their digital safety, and watch your incident reporting rates climb.
7. Keep the momentum going
Memory fades fast. Use October to kick off year-round nudges, quick blog posts, and lightweight updates that keep security top-of-mind.
So, in this blog, we tackle the burning questions many cyber pros ask themselves as October 2026 approaches:
Why is cybersecurity awareness month important?
How can I make it impactful and drive meaningful change?
How can I ensure awareness of cybersecurity risks and promote self-protection?
What mistakes should I avoid for a successful cybersecurity awareness month?
How can I engage and inspire others about cybersecurity?
How does behavioural science apply to leading a successful CAM?
How do I tailor messages to different audiences and knowledge levels?
How can I use social influence to foster a strong security culture?
How can I make the consequences of security breaches tangible and relevant?
Does gamification, positive reinforcement, and autonomy actually boost engagement?
Cybersecurity Awareness Month is your chance to make a difference. And this guide is about to make it easy. Impactful. Fun. Memorable.
Why is Cybersecurity Awareness Month important?
There are tons of reasons why cybersecurity awareness is important. Here are some of the biggest ones:
Cyber attacks are on the rise. The number of cyber attacks has been increasing in recent years, and the cost of these attacks is also on the up. In Oh, Behave!, our annual study with the National Cybersecurity Alliance, 45% of the 7,000 people we surveyed said advice on staying secure online is confusing. That confusion is what attackers bank on.
The human factor is a major contributing factor. Even the most secure systems can be compromised by the wrong behaviour.
Cybersecurity needs everyone’s support. It’s not just cybersecurity and IT professionals. Everyone has a role in protecting their organisations and themselves.
You and your team may have overall responsibility for protecting your organisation.
But you can’t do it alone.
That’s why it’s important for everyone to be aware of cybersecurity risks and to take steps to protect themselves…and their organisation.
Part 1: Why AI must be in your 2026 CAM plan
Our Oh, Behave! report, run with the National Cybersecurity Alliance, surveyed 5,000 people.
An overwhelming 80% of adults now use AI tools daily, and half of all workers use them on the job …mostly on their own initiative. But corporate guardrails haven't caught up: 52% of employees using AI have received zero security training on it.
The result? Workplace Shadow AI is running rampant. One-third of workers admit to copy-pasting confidential company data into public AI bots without their boss ever knowing.
On a personal level, users are routinely confessing their deep secrets, health records, passwords, and even banking details to chatbots. We’re worried about AI cybercrime, sure – 67% of us fear AI-driven scams – but that hasn't stopped us from treating the chatbot like a digital therapist and administrative assistant all rolled into one.
Which is why running a 2026 security campaign without addressing AI is like running a campaign in 2010 and ignoring the internet. (I.e, not clever).
And remember: people don't need another dense 10-page AI policy document. They need three basic habits:
Check what you’re pasting.
Assume public chatbots aren't private.
Ask before uploading work files.
(easy) AI activities for October:
Run an AI amnesty: Ask your team to anonymously share what they’ve pasted into chatbots …with a strict zero-blame guarantee. You’ll learn more in an hour than any survey could tell you.
Play a CEO deepfake: Play a fake voice note from leadership to show how convincing impersonation has become.
Create team AI norms: Spend 15 minutes drafting a single page of AI guidelines written by the team, not handed down from legal.
Host a prompt-safety clinic: Have staff bring real prompts to review what’s safe to keep and what needs to be scrubbed.
Part 2: Planning for value, impact, and proof
Every year during Cybersecurity Awareness Month, amazing work is done by the community to support, guide and educate people, to highlight new threats, to reinforce best practice, and to strengthen relationships within organisations.
But…
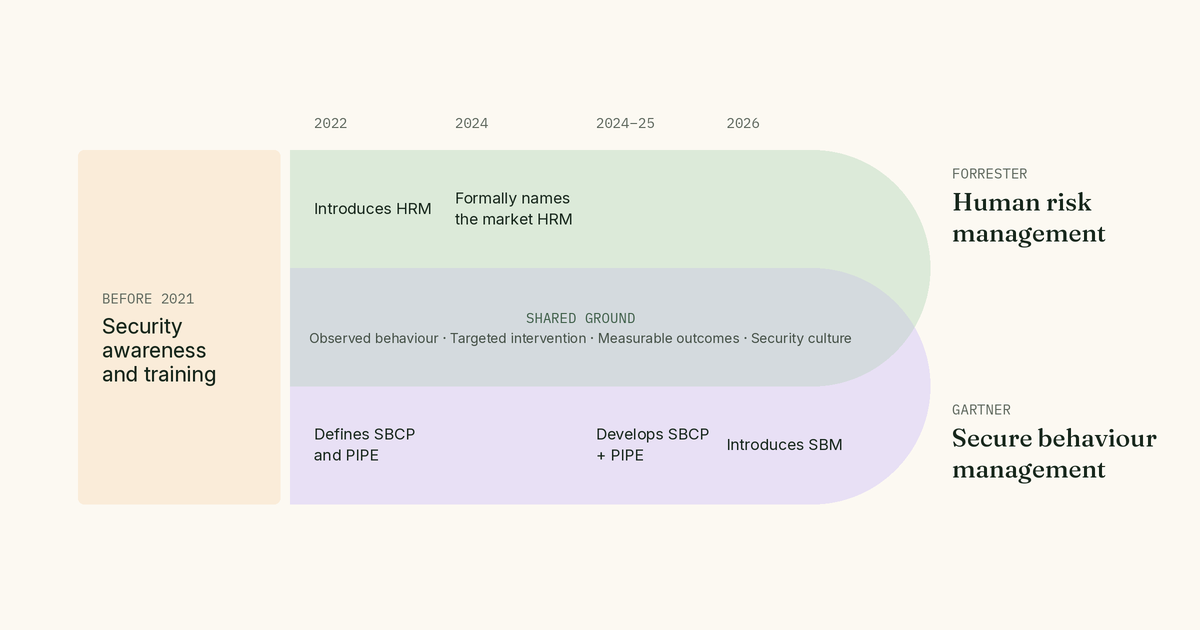
One of the biggest differences between Human Risk Management and Security Awareness & Training, is planning the impact of your activities-beyond ticking the compliance box-before you start.
What is it you’re trying to achieve?
Which security behaviours do you want to influence?
Which business risks are you going to reduce?
Taking the time to understand this before you start your Cybersecurity Awareness Month planning will make it much easier to demonstrate the value of your activities when you’re done.
Part 3: Free Cybersecurity Awareness Month resources
50 activity ideas for Cybersecurity Awareness Month 2026
Need inspiration? Mix and match these 50 ideas to build your custom month-long itinerary:
Play security bingo: Use ready-made cards or create a custom version tailored to your company's internal jokes and software.
Host a lunch and learn: Casual vibes, free pizza, real security discussions.
Run a meme contest: Let your team turn their daily IT annoyances into comedy.
Film a PSA video: Short, punchy, and shared on internal channels.
Launch security champions: Recruit representatives from sales, HR, and ops (snack incentives strongly recommended).
Answer real FAQs on video: Record your security team answering the top 5 questions people are (usually) afraid to ask.
Kick off new training: Use the October spotlight to debut updated learning modules.
Intranet takeover: Feature rotating security tips on your homepage banner.
Social media blitz: Encourage employees to share their favorite digital safety tips publicly.
Write cyber horror stories: It is October, after all… Challenge people to write 100-word thrillers about losing their unbacked-up work.
Revamp onboarding: Ensure new hires get a warm, practical security intro from day one.
Digital escape room: Challenge teams to solve security puzzles to ‘escape’.
Cyber scavenger hunt: Hide clues across internal wikis or physical office spaces.
Breakroom board games: Leave custom security trivia board games in common spaces.
Digital comic book: Publish a short graphic novel highlighting common social engineering tricks.
Podcast episodes: Record a 10-minute interview with a guest speaker or internal expert.
Host an on-demand webinar: Walk through practical threat-prevention strategies live.
Newsletter takeover: Dedicate your weekly company bulletin entirely to October's theme.
Publish a resource guide: Create a downloadable 1-pager for remote workers.
Security mentors: Pair new employees with seasoned champions for their first month.
Recognise safe behaviours: Highlight departments with the highest scam-reporting rates during performance reviews.
Run a month-end quiz: Host a live Kahoot! with real prizes for the top scores.
Security ‘office hours’: Hold open drop-in hours where anyone can ask tech questions guilt-free.
Themed canteen menu: Offer ‘balti-factor authentication’ or ‘phish and chips’ at lunch.
Security selfies: Reward staff for sharing pictures of their clean desks and locked screens.
Hack-along sessions: Show a safe, simulated demonstration of how credential harvesting works.
Daily micro-tips: Post a one-sentence tip every morning on Slack or Teams.
Live attack simulations: Walk through a realistic breach narrative step-by-step.
Family tech day: Host a session showing employees how to lock down personal devices and parental controls at home.
Kids' security resources: Share fun activity books for parents to pass along to their kids.
Leadership mini-talks: Get department heads to spend 3 minutes at the start of team meetings talking about security.
Password cracking demos: Show live estimates of how fast weak passwords get cracked vs. passphrases.
Film night: Watch The Net (1995) or Sneakers and count how many security mistakes the characters make.
‘Meet the security team’ video: Put faces to names, so your team feels comfortable reaching out when something goes wrong.
Guest speakers: Invite an outside ethical hacker or industry expert for a Q&A.
Dedicated awareness day: Clear an afternoon for short, interactive workshops.
OSINT workshop: Show staff how much personal information is publicly available online with a live OSINT demo.
Myth-busting sessions: Clear up common misconceptions (like ‘incognito mode hides everything’).
Custom video backgrounds: Supply fun security-themed backgrounds for video calls.
Swag (that people actually want): Quality stickers, screen cleansers, or webcam covers (but you know your team best)
Department ambassadors: Give vocal/enthusiastic team members official ambassador roles.
Digital badges: Award email signature badges for completing October activities.
Focus on wellbeing: Connect digital security to mental peace-of-mind and stress reduction.
Think like an attacker: Walk through how social engineers choose their targets.
Cyber book club: Pick a readable tech thriller or non-fiction book for the month.
‘Security is everyone’s job’ video: Feature short clips of staff across different roles sharing what they do to stay safe.
Phishing simulation games: Interactive, non-punitive exercises to spot fake headers and URLs.
Storytelling weeks: Break the month into 4 themes, such as: Physical Access, Phishing, AI Safety, and Password Health.
Cryptic teasers: Leave mysterious digital or physical clues around the office leading to a campaign reveal.
UK focus – localised case studies: For UK-based teams, dive into local insights using regional stats from NCSC and CybSafe research.
At the end of the day, you can pick and choose. This is just a starting point. You know what will work best for your team, and you’re more than capable of choosing activities that will fit your needs and engage your people.
---
The security awareness toolkit: must-have resources to boost your campaign
At CybSafe, we take pride in our science-based, expert-led approach to cybersecurity. It’s been proven to be highly effective in helping organisations reduce their risk of cyberattacks.
And, frankly, this is too good not to share, so we’re dropping the link here.
Security awareness blogs
Exclusive to the toolkit, access to eight story-style blogs:
Are you really a target? guides people through how to assess their risk and take steps to protect themselves.
Security incidents: Your role helps people understand their role in responding to security incidents.
Passphrases helps people to use and remember strong, unique passphrases.
Working remotely looks at safe practices for working outside of the workplace.
Spotting fake emails, featuring James Linton will transform people into laser-eyed fake-email-spotting pros.
Sophisticated attacks shows people how to identify and defend against the latest, social engineering attacks.
Protecting your devices helps people keep their devices safe from malware and other threats.
Preventing identity theft explores how people can protect their personal information.
Our latest studies
If you're building a business case for your campaign budget, don't rely on generic statistics. Ground your strategy in data from our latest studies:
The reality check: Only 23% of employees currently know CAM exists, and just 15% say their employer actively involves them.
The good news: 93% of active participants feel their company takes security seriously, and 80% say participating directly changed how they behave online.
The Oh, Behave! annual report. Our joint research with the NCA showing where workers struggle most with digital security habits.
---
Part 4: Tips, tricks and things to avoid
There have been many inventive CAM campaigns over the years, but here are a few of our favourites…
Creative CAM campaigns that made a splash
The University of California, Berkeley created a Cybersecurity Scavenger Hunt that challenged students to find hidden security vulnerabilities on campus. We love how they used gamification to make it fun and engaging for students to learn about cybersecurity risks. This taps into the psychology of motivation, as people are more likely to learn and retain information when they’re having fun.
The City of San Francisco created a cybersecurity comic book that told the story of a group of hackers who try to steal the city’s data. This was a creative way to reach out to a younger audience and teach them about cybersecurity risks. This uses narrative persuasion, which is a powerful way to communicate information because it appeals to our emotions and helps us to understand complex concepts.
The National Cybersecurity Alliance created a cybersecurity selfie challenge that encouraged people to take selfies with cybersecurity messages. This was a fun and social way to raise awareness of cybersecurity risks. This uses social proof, which is the tendency for people to follow the lead of others. When we see that other people are taking selfies with cybersecurity messages, we’re more likely to do the same.
The University of Texas at Austin created a cybersecurity escape room that challenged students to solve puzzles and find clues in order to escape from a locked room. This was a fun and interactive way to teach students about cybersecurity risks. This uses experiential learning, which is a type of learning that occurs when we actively participate in an activity. This type of learning is often more effective than traditional forms of learning, such as reading or listening to lectures.
The Seattle Public Library created a cybersecurity trivia night that challenged people to answer questions about cybersecurity. This was a fun and social way to raise awareness of cybersecurity risks. This uses gamification, which is the use of game-like elements in non-game contexts. Gamification can be a great way to make learning more fun and engaging.
Capital One created a cybersecurity training arcade that allowed employees to learn about cybersecurity risks in a fun and interactive way. This was a great way to engage employees and teach them about phishing, malware, and other cybersecurity threats. This uses operant conditioning, which is a type of learning that occurs when we’re rewarded for our behaviour. When employees are rewarded for learning about cybersecurity, they’re more likely to continue learning and practising safe behaviours.
Visa created a cybersecurity theatre that put on a series of plays about cybersecurity risks. This was a creative way to reach out to a wider audience and teach them about cybersecurity risks. Like the comic book, this used narrative persuasion to great effect.
The ‘This is Personal’ campaign by the UK government is a powerful campaign that highlights the human cost of cyberattacks. This campaign features real-life stories of people who have been affected by cyberattacks. It’s been praised for its emotional impact. This uses emotional appeals, which are a powerful way to persuade people.
These are just a few of the many inventive CAM campaigns that have tickled our fancy. They demonstrate the power of creativity and innovation in raising awareness of cybersecurity risks.
5 (scarily common) CAM mistakes to avoid
Prepping at the last minute: Rushed campaigns feel chaotic. Start drafting your high-level plan early in the year so you aren't scrambling in late September.
Overcomplicating things: You don't need to cover every threat vector ever invented. Focus on core daily behaviors. Repetition of simple habits beats a flood of complex information.
Assuming people remember last year: Just because a topic was covered 12 months ago doesn't mean it stuck. Refresh the basics without being patronizing.
Forgetting to budget: Engaging activities, quality swag, or external speakers require resources. Plan your budget early so you can amplify your reach.
Making it dry: Cybersecurity is serious, but learning about it doesn't have to feel like a penalty. Make the experience interactive, memorable, and human.
If you sidestep these hurdles and sprinkle some behavioural science, creativity, and innovation into your cybersecurity awareness campaigns, you’ll be well on your way to success.
Tips from the pros!
We also asked our panel of pros to explain what has worked well for them in past years. Here’s what they hit us with:
Junell Felsburg, Sr. Director of Cyber Security and Infrastructure, The Columbus Foundation
“While it is easy to assume everyone shares the same foundational understanding of cybersecurity, the truth is each individual brings their unique perspective and experiences to the table. As cybersecurity professionals, we must recognize this diversity as the strength it is, and tailor our messaging accordingly.
Using storytelling, we can transform complex concepts like threat and risk management into captivating tales that resonate with our audience. For instance, we might liken the challenges of defending against cyber threats to the heroic struggles of knights protecting an ancient castle, or use a narrative of cunning assassins to illustrate the dangers of phishing attacks.
But storytelling isn’t just about entertainment—it’s about engagement and empowerment. By sparking curiosity and fostering a deeper understanding of cybersecurity issues, we can encourage our communities to ask questions, seek further knowledge, and take proactive steps to enhance their digital safety.”
Stu Walton, Deputy Director of Digital & IT Services, Newman University
“While we’d love all our staff to have the intrinsic motivation to behave safely and engage in activities over Cyber Awareness Month, we know sometimes they need a little recognition for the additional engagement they give throughout the month.
When it came to running my first Cyber Awareness Month, I gave out certificates to participants for the events we had on. All staff who had engaged with us over the month got a signed certificate, hand-delivered.
Admittedly, we are a single-site campus where nowhere is more than five minutes’ walk, but it was amazingly effective. Walking into shared offices with a sheaf of certificates and handing them to staff was great for me and them, because I got to see the joy on their faces for recognizing their contribution. Not to mention their colleagues who didn’t get one asking why, and I could then point them to additional resources or any activities we had coming up.
The personal touch was really in keeping with our organizational culture and made a big impression. So much of our work and communication is digital; I think people really liked having something tangible to show for it. I’ve since discovered that they love pin badges, too!”
James Mountford, Security Awareness & Culture Lead, AVEVA
“Running an inclusive and engaging security awareness month encourages autonomy and ownership within our workforce. We had a variety of activities for colleagues to participate in.
By offering a range of options and training opportunities, employees are empowered to take ownership of their own security journey. Participation in these initiatives not only equips employees with the necessary knowledge and resources, but also instils a culture where reporting suspicious activities is encouraged and celebrated. This multifaceted approach helps colleagues feel in control of their own security, which makes them more likely to report suspicious activity and create a safer digital and physical space.”
Nick Allen, Information Security Specialist, Just Eat Takeaway
“After using SebDB to target our key behaviors, we were able to implement nudges as a form of light reinforcement for colleagues, and saw an enormous change in behavior as a result.”
Louise Cockburn, Information Security Awareness and Culture Manager
"Last year as part of our CAM events, we put together a series of videos and a panel talk from some of our security operations team. They talked about their experiences with common security attacks, like account takeovers and social engineering, and the habits they formed to combat these threats. Kind of a, “I work in Security and this is one thing I ALWAYS/NEVER do!”
Stories and storytelling are really effective ways to impart messages – especially around topics that can feel dull, technical, scary, or abstract. We found that hearing what our team of very technical and skilled security pros have witnessed or even experienced themselves was really impactful, creating a lot of engagement and discussion in both the video comments and during the panel talk (the themes of which were great qualitative metrics for us to note!).
Not only that, but it helped ‘humanise’ security as a function – which can often be perceived as a bit intimidating and unapproachable.
From a social proof point of view, if someone who works full time in security has been sufficiently moved to make a habit change and says a certain habit or behaviour is a MUST, it lands with clout, and harnesses that persuasive “appeal-to-ethos” effect (we’ve seen a similar effect with talks and webinars we hosted featuring subject matter experts from a variety of fields).
As an event, this was a very simple case of having some of the team do a very informal video which we then edited and published internally over the course of the month. The panel we hosted through Teams, and used the corporate calendar, email, and comms channels to publicise.
Metrics & measurements of success:
Running cybersecurity awareness month in the UK
Cybersecurity Awareness Month may be a global campaign, but it works best when it feels relevant to the people taking part. For UK organisations, this means using situations employees genuinely recognise from their working lives.
Think about the kinds of threats people encounter every day: a convincing Microsoft 365 login request, a fake supplier invoice, an urgent Teams message that appears to come from the managing director, or a parcel delivery text sent to a personal phone. When examples feel real, people are more likely to remember what to do when a genuine threat appears.
It’s worth thinking about timing, too. October is often a busy month, and the autumn half-term can interrupt your campaign just as it gets going. Promote activities early, spread them across the month and give people different ways to join in, whether they work in an office, from home or on the move.
The UK practitioners featured in this guide, including Stu Walton at Newman University and James Mountford at AVEVA, show that effective awareness programmes don’t need to rely on fear. Personal recognition, relatable stories and simple opportunities to participate can do far more to change behaviour than another warning about regulatory fines.
Above all, Cybersecurity Awareness Month shouldn’t feel like four weeks of warnings and compulsory training. CybSafe recommends using it to start useful conversations, build practical security habits and give people positive reasons to take part. Relatable stories, well-timed nudges and a little personal recognition can help cybersecurity feel like part of everyday working life, not another box to tick.
Before we go
Let’s say it again (for the people at the back): You have the power to make a real difference here. By being smart about your CAM game, you can upgrade your organisation’s security posture and inspire people to take steps to protect themselves and your organisation.
We believe that people are the key to iron-clad cybersecurity. Which is why our solutions are engaging, educational, and effective. (And frankly, if you haven’t booked a demo yet, what are you waiting for?)
Chances are your brain is bursting with ideas by now, and you’re in planning mode. We’d love to know how your CAM went down and what you got up to, so feel free to tag us in your socials so we can live vicariously through you.
Here’s to securing our world, and making #CAM2026 count.
---
Cybersecurity Awareness Month FAQs
When is Cybersecurity Awareness Month?
Cybersecurity Awareness Month is observed every year in the month of October. It is a month-long initiative filled with activities, events, and educational efforts to promote cybersecurity awareness.
When did Cybersecurity Awareness Month start?
National Cybersecurity Awareness Month, often referred to as CAM, began in 2004. It was initiated by the National Cyber Security Alliance (NCSA) in the United States. Since then, it has grown into a global event, with millions of organisations participating to promote cybersecurity awareness and education.
What is Cybersecurity Awareness Month?
Cybersecurity Awareness Month (CAM) is an annual global campaign dedicated to raising awareness about the importance of cybersecurity. It aims to educate individuals and organisations about cybersecurity risks, best practices, and how to protect themselves from cyber threats.
What is CISA Cybersecurity Awareness Month?
CISA (Cybersecurity and Infrastructure Security Agency) Cybersecurity Awareness Month is an initiative by the U.S. federal government, specifically led by CISA. It is a part of the broader Cybersecurity Awareness Month and focuses on promoting cybersecurity best practices, resources, and information within the United States.
What is a Cybersecurity Awareness Month toolkit?
A Cybersecurity Awareness Month toolkit is a collection of resources, materials, and guides that individuals and organisations can use to support their cybersecurity awareness campaigns during October. These toolkits typically include posters, templates, social media content, and educational materials to help promote cybersecurity awareness effectively. For example, you can find valuable resources like the Security awareness engagement toolkit.
What are the themes for Cybersecurity Awareness Month in 2026?
Cybersecurity Awareness Month features different themes each year to focus on specific aspects of cybersecurity. The 2026 theme is ‘Don’t make it easy for them’, and it focuses on the everyday habits that make an attacker’s job harder.
Learn more with SebDB
Each habit maps to a measurable behaviour in SebDB, CybSafe's open database of security behaviours. Use these to plan what you measure, and to show what changed.
These themes reflect the commitment to building a more secure, interconnected world.
Ready to make 2026 your best campaign yet?
Building a security-conscious workforce isn't about ticking compliance boxes. It's about helping your people build small, everyday habits that keep them (and your organisation) safe.