The engagement
The security team had a clear challenge. They wanted to align to the CAF EP in a robust and strategic way. Through their learning content they aimed to be recording videos, hosting them on SharePoint, chasing completions through forms and spreadsheets, but that was eating up roughly 30 hours every month.
They needed a platform that could help them align to the CAF EP framework, deploy learning fast, automate the follow-up, and give them time back to focus on the work that actually reduces risk.
What they built with CybSafe
Automated workflows that replaced manual effort
No-code workflows for phishing follow-up, staggered learning assignment, manager escalation, and credential harvest remediation. These workflows now save 6–7 hours a month on admin alone, and they're still building more.
Rapid deployment through Teams messaging
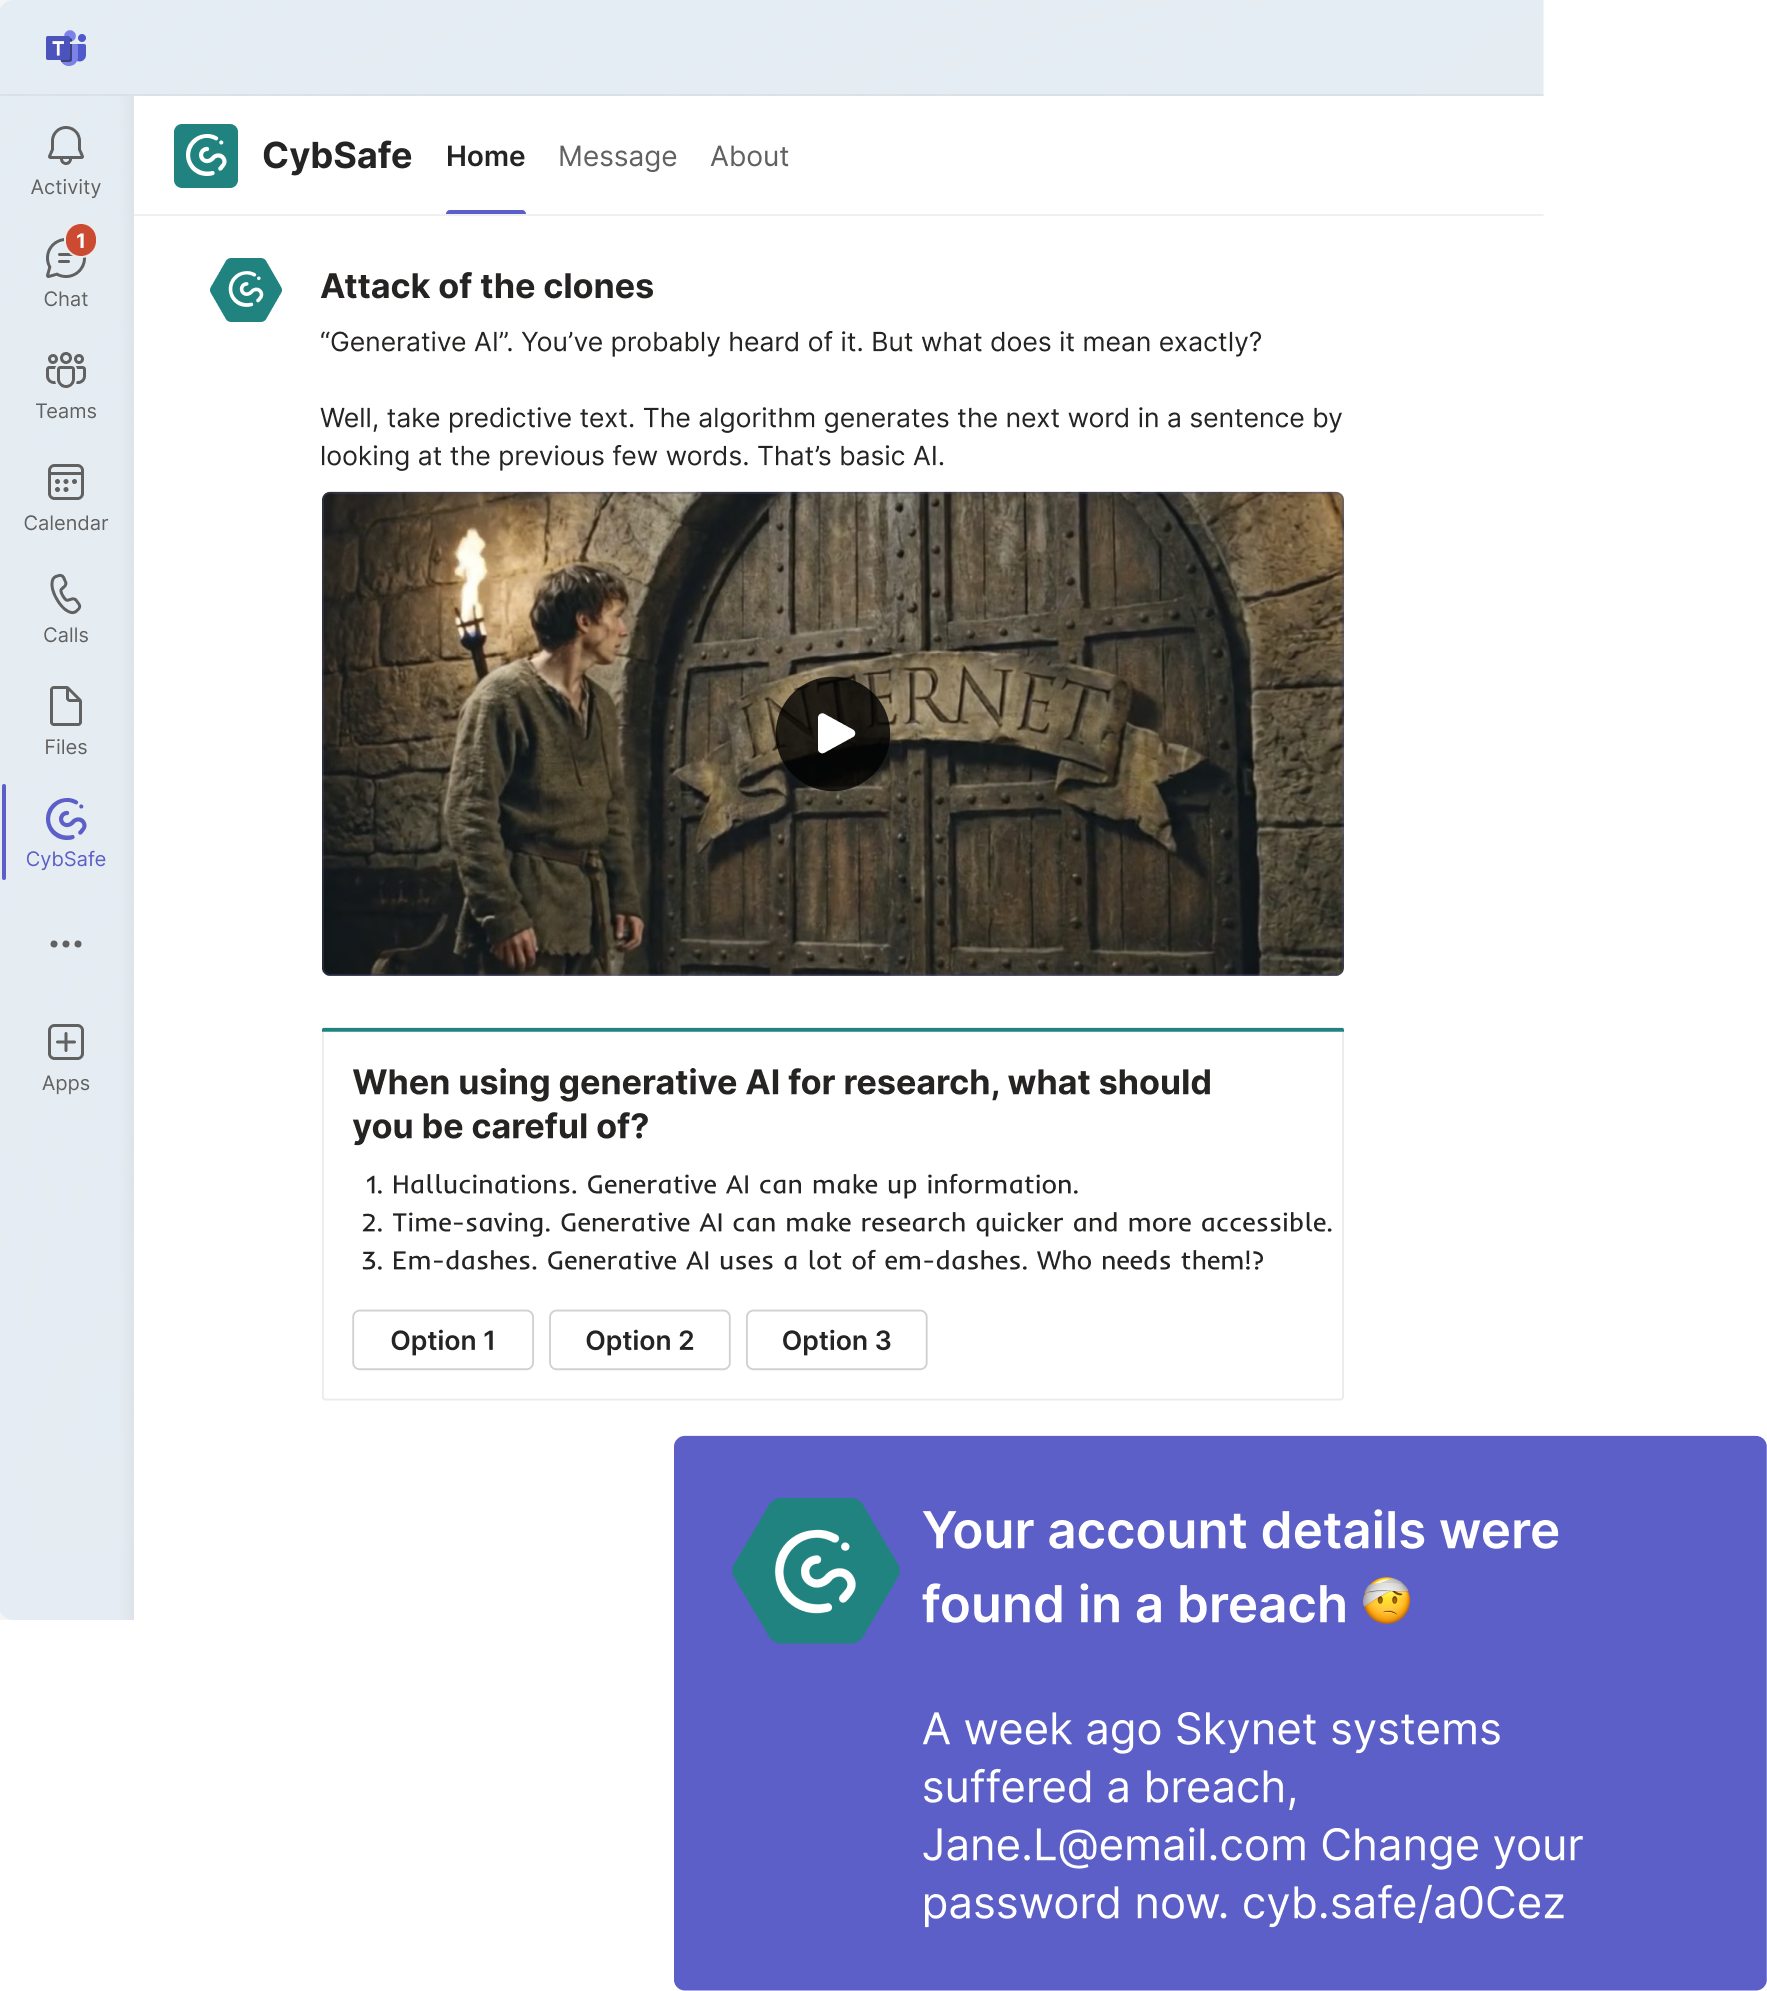
CybSafe's integration with Microsoft Teams gave them the ability to reach the entire organisation instantly with targeted messages. This is now a core part of their rapid-response process.
Director-level reporting and visibility
They paired CybSafe's API to create dashboards, giving each directorate monthly automated reporting on key security behaviours. Competitive leaderboards across business units turned security metrics into a leadership conversation, not just a security one.
A proven rapid-response process
As a UK energy company, they need to move fast when social engineering threats target their people. Through previous incidents, the security team has pressure-tested a rapid-response process using CybSafe, and it's now their standard playbook.
The process is straightforward: when a threat emerges, the team deploys targeted communications and learning through CybSafe within hours. Leadership-backed messaging reinforces urgency. Automated nudge workflows chase completions daily, escalating to managers and, where needed, flagging account suspension. No manual follow-up required.
- 73% completion within 48 hours
- 96.9% final completion rate achieved
- ~6,000 people reached across the organisation
These numbers aren't targets. They're results from real deployments. And because the process is now repeatable (workflows built, escalation paths set, communications templated), each future response gets faster than the last.
The process also exposed a gap worth fixing: people weren't always sure how to report a suspicious phone call the way they would a suspicious email. They built a dedicated internal reporting route so that non-email threats can be flagged just as quickly. That's the mindset: use each response to make the next one better.
Time saved: the numbers
The security team quantified the operational impact of CybSafe across two dimensions:
- 30 hours per month saved on learning deployment. Without CybSafe, the team would have to record videos, host them on SharePoint, build tracking forms, and manually chase completions. That entire process is now automated in CybSafe.
- 6–7 hours per month saved on workflow administration. Phishing follow-ups, escalation paths, and nudge sequences now run without manual intervention, freeing the team to focus on risk, not admin.
- Faster time to deployment. The internal LMS route through L&D would have taken longer to stand up. CybSafe was operational in a fraction of that time.
What this looks like in practice
Their experience shows what happens when a security team treats awareness as an operational capability, not a compliance checkbox.
They move fast when threats emerge. They automate the follow-up so nothing slips. They report to leadership with evidence, not anecdotes. And they keep improving: building new workflows, strengthening reporting pathways, and growing the team who run the programme independently.
That's the shift CybSafe enables: from programme to capability.

30 hrs
saved per month vs manual delivery
6–7 hrs
saved per month on workflow admin
73%
completion within 48 hours at scale
96.9%
final completion rate achieved
~6,000
people reached in a single deployment